
How to certify a web page so it can serve as evidence
Certifying a web page means preserving its content as it appears at a given moment, along with the information needed to verify its origin and integrity. You can take a screenshot, engage a notary or a digital forensics expert, or use forensic acquisition software. Each approach offers different safeguards. This guide explains what they are.
A listing, a post, a price list, a review: whoever published them can change or delete them in seconds. If you need the page as evidence, preserve it before it is edited or removed.
What “certifying” a web page means
The term covers several different processes. To understand the options, it helps to distinguish three concepts:
- the certified copy issued by a notary, who attests to what was displayed on the page at that moment;
- the timestamp, a date applied by a third party to a set of data. When it is qualified under the EU eIDAS Regulation, it benefits from a presumption that the date and time are accurate and that the data it covers is intact (Art. 41(2)). It concerns the date and the integrity of the data: it does not identify who carried out the acquisition and does not attest that the content is true;
- forensic acquisition, the process of capturing the page and the technical data needed to examine it: code, resources, traffic, certificates and hashes.
None of these approaches makes evidence “indisputable”: its weight is for the court to assess. The aim is to collect material that others can verify.
Four ways to preserve a web page
| Method | What it preserves | Limitations | Subsequent verification | Cost |
|---|---|---|---|---|
| Screenshot or PDF printout | How the page looked when it was captured | On their own, they provide no independent verification of the date, origin or integrity | Comparison with the original may become impossible if the page changes | None |
| Notary’s certified copy | What the notary sees on the page at that moment, attested by a public official | Does not cover code, traffic or technical provenance data; video and audio require separate consideration | Relies on the notary’s attestation | Notary’s fee |
| Report by a forensic expert | A technical acquisition, with a report by a professional who can explain it in court | Depends on the tool and method the expert uses | Another expert can examine the supplied data | Quoted individually |
| Forensic acquisition software | Screenshots, code, a replayable archive, traffic, certificates, hashes and a timestamp | The operator’s identity is self-declared; expert assistance must be arranged separately | Whoever receives the bundle, if the product includes independent verification tools | From a few euros per acquisition to annual licences, depending on the product |
The screenshot
A screenshot preserves how the page looked, but on its own it does not let anyone check its origin or when it was taken. It can be produced in court; if it is challenged, additional evidence may be needed to show that it faithfully represents what was online. We cover this in Does a screenshot hold up in court?
The notary
The notary opens the page and issues a certified copy of what is displayed. That attestation carries the weight of an act by a public official. Its scope matters, though. In Italy, according to Infonews Notartel, an Italian notarial publication covering technology, the copy covers textual content; if the page includes video or audio, the copy is only partial, and those elements require an expert’s report. Rules differ from country to country. This approach may be suitable when a public official’s attestation is the main requirement and the material is static and limited in scope.
The forensic expert
A digital forensics expert acquires the page with forensic tools and writes a report describing what was done and how. The expert also interprets the data and explains the method used. When appointed by a party to the proceedings, they can answer questions from the court and the opposing party. This is particularly useful in complex cases, when the evidence is likely to be challenged or when the data requires analysis. For more detail, read Forensic expert or self-service capture?
The software
Forensic acquisition software automates the technical steps of evidence collection: it opens the page in a controlled environment, records the content, hashes the files and applies a timestamp, depending on the features of the product chosen.
It lets you act even when a professional is not immediately available. The material can be examined later by an expert, who will decide how to use and present it. To compare the options, read Forensic web page acquisition software: how to choose.
What a forensic acquisition should contain
Whichever tool or professional you choose, check what the final bundle includes. Here are the key elements to look for and why they matter.
- Screenshots of both the visible area and the full page: these show how the captured content appeared.
- The page’s code after it has loaded. Many sites build their content in the browser: the source sent by the server may, on its own, be almost empty.
- An archive of the browsing session (in our case in WACZ format), which can be reopened and inspected even when the site no longer exists.
- The traffic exchanged with the server: the list of every request and response (HAR format). It shows what the site actually sent, and from which addresses.
- Provenance data: which IP address the domain resolved to (DNS), who it is registered to (WHOIS) and the TLS certificate the site presented — the “padlock” that ties that content to that domain at that moment.
- The time, taken from an external source and not from the computer’s clock.
- File hashes for every file: if even one character changes, the hash no longer matches.
- A timestamp applied by a third party to the list of hashes.
- Verification tools, to check the bundle independently of whoever produced it.
The full list of what C.E.R.T.O. produces, file by file, is on the Web pages module page.
Acquiring a web page with C.E.R.T.O., step by step
- Register and confirm your email address. After confirming your email address, you receive 2 free slots, enough for one web acquisition.
- Install C.E.R.T.O. on your computer (64-bit Windows or a Mac with Apple silicon) and sign in with your account.
- Open the Web pages module and navigate to the page in the built-in browser, then press “Start Acquisition”. Before starting, specify two details that will be included in the report: the scope (a single page, the domain with its subdomains, or free navigation) and the subject, a short description of what you are acquiring and why.
- Browse as you normally would. Each session supports up to ten pages. If you need more, split the work across several acquisitions. If the page requires signing in to an account, use your own credentials. Each page you visit is captured as evidence. For social media posts, comments are collected from the platform’s data source rather than captured solely as images.
- Finish the acquisition. C.E.R.T.O. hashes every file, signs the inventory, requests two timestamps and packages the bundle. If you need the qualified eIDAS timestamp, enable it before starting the acquisition, in the built-in browser’s settings (the gear icon).
- Receive the evidence bundle: a compressed folder with the PDF report, a dashboard that opens with a double click and the verification tools.
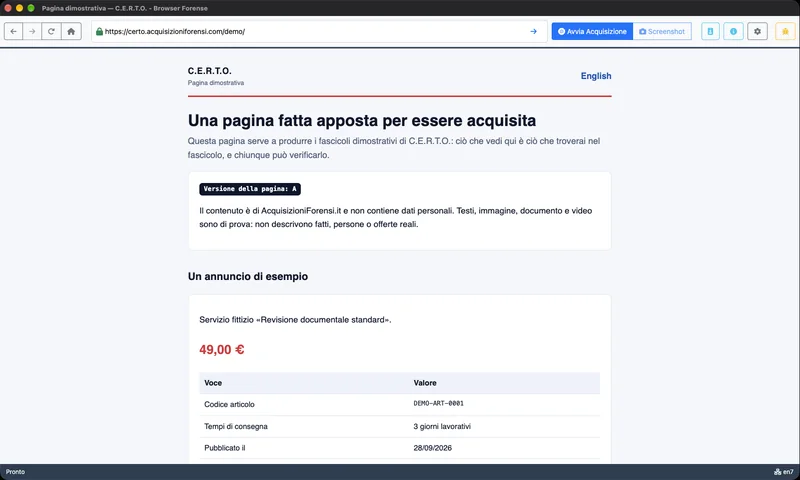
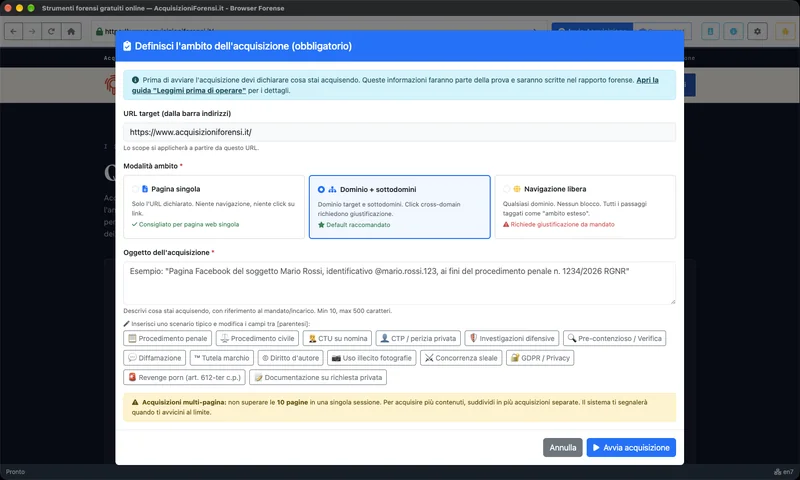
A web page acquisition costs 2 slots, even if you visit several pages in the same session; 4 slots with the qualified timestamp. A slot costs between €3 and €6 depending on the package: current prices are on the pricing page. There are no subscriptions and slots do not expire.
How to verify an evidence bundle
The bundle includes the tools to recalculate the hashes and check the signature and the timestamps: verify.sh for Mac and Linux, verify.bat for Windows, and a dashboard for reviewing the contents and checking file integrity. The checks establish whether the content matches what was sealed when the acquisition ended.
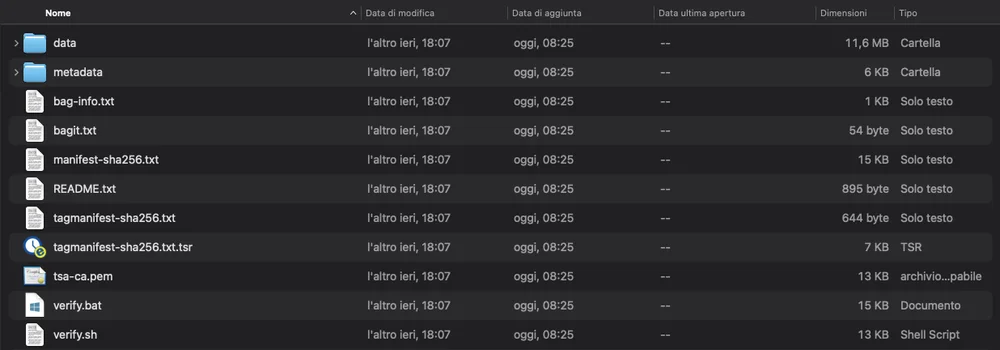
Recipients can verify the bundle without installing C.E.R.T.O. The requirements vary by check:
- recalculating the hashes can be done offline;
- checking the signature and timestamps requires OpenSSL 3. If it is missing on a Mac, the script downloads a small verification kit from our website and checks its hash before use. This one-time download requires an Internet connection. On Windows, follow the instructions in the bundle’s
README.txt. If the required software is unavailable, these checks are marked not performed, rather than failed; - finally, the script queries our online registry to confirm that the acquisition is on record. This optional step requires an Internet connection and can be disabled.
On Mac and Linux, open the Terminal, navigate to the bundle folder and type:
sh verify.shThe command sh verify.sh starts the script even if the file extracted from the archive lacks execute permission. If you run ./verify.sh and get permission denied, use the command above instead. On Windows, double-click verify.bat.
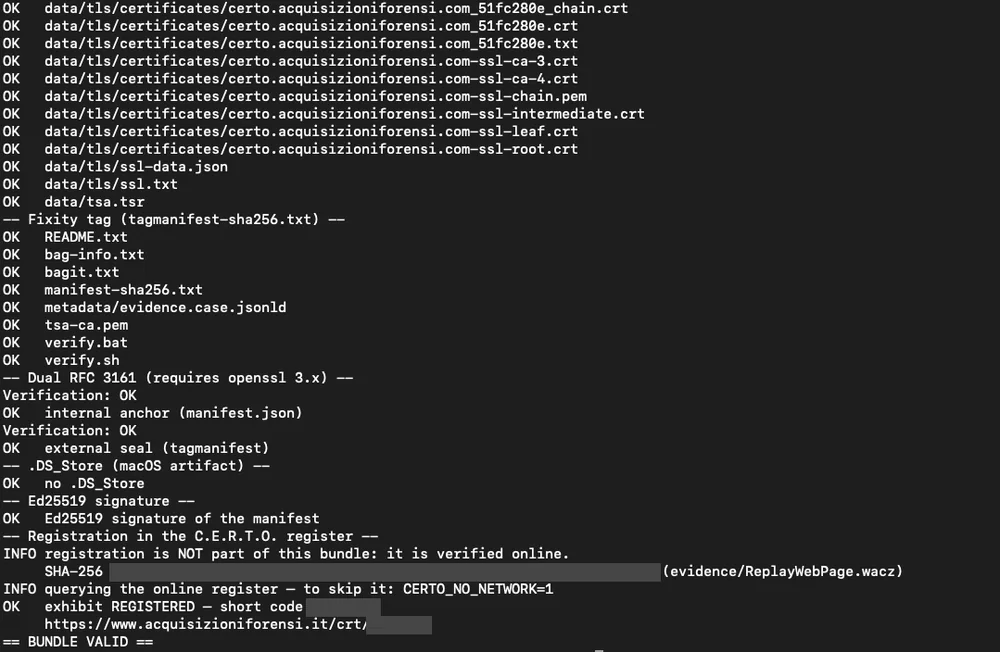
If you would rather not use the Terminal, open the bundle’s dashboard with a double click and use the integrity verification section: it recalculates the hashes of every file directly in the browser.
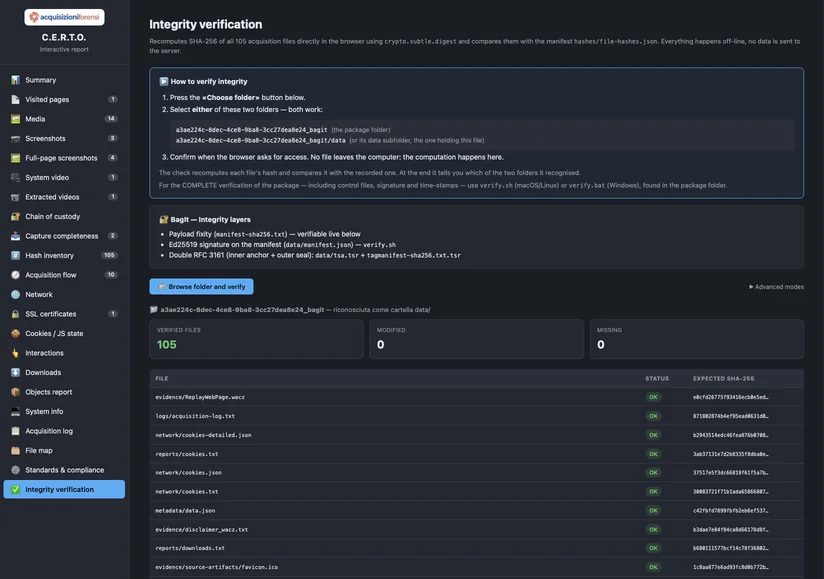
You can see what it looks like before registering: the How it works page has two sample bundles to download. The verification procedure is described in How the opposing party can verify digital evidence.
What an acquisition does not prove
To use the material properly, it is essential to know its limits as well.
- It does not prove the content is true. It proves that the site, at that moment, displayed it.
- It does not prove who wrote it. A profile may be fake or used by someone else: linking the content to a specific person requires additional evidence.
- It does not prove how long the page had been online, nor that it stayed there afterwards. Where needed, you can capture the page at two different times and compare the two bundles.
- It does not recover what has already been deleted.
Frequently asked questions
Does a certified web page have legal value?
It can be produced as evidence, and a document cannot be excluded merely because it is electronic. The court assesses its evidential weight, taking into account the safeguards for its security and integrity. The qualified eIDAS timestamp adds a presumption about the date and the integrity of the timestamped data; it does not turn the content into an established fact.
What is the difference between a certified copy and a forensic acquisition?
A certified copy is an attestation: a public official, usually a notary, attests that the copy matches what they observed. Forensic acquisition is a technical evidence-gathering process: it preserves the page together with the data that let anyone verify it. A certified copy relies on the authority of the official; forensic acquisition relies on technical verification. They can also be used together.
Does the Wayback Machine count as evidence?
The Wayback Machine, run by the Internet Archive, can help reconstruct what a website displayed in the past. You cannot, however, choose retrospectively what was saved or when. The page you need may be missing, incomplete or captured on a different date, and content behind a login is not available. Use it to reconstruct a site’s history — our website history service does that — and make your own acquisition of content that is online today.
Can a page that has already been deleted be certified?
No: you acquire what the site shows at the moment you visit it. If a page has been removed, you can look for archived copies and acquire those, making their source clear. If the content is still online, preserve it before contacting the other party.
Can social media posts and comments be certified?
Yes. With C.E.R.T.O. the Web pages module automatically recognises Instagram, Facebook, TikTok, X, YouTube, Google Maps reviews, and conversations in Messenger and Instagram Direct. Comments and replies on posts are collected from the same source the platform uses to display them, rather than captured solely as images. One common use is preserving a defamatory review.
How much does it cost to certify a web page?
It depends on the method. With C.E.R.T.O. an acquisition costs 2 slots, 4 with the qualified timestamp: a slot costs between €3 and €6 depending on the package, and the first acquisition is covered by the 2 welcome slots. Notaries and forensic experts charge professional fees, usually based on a quotation.
Do I still need a forensic expert?
Not always. You can independently capture content that is at risk of removal. If it is likely to be central to a case, consider engaging an expert to examine it and explain the findings. The bundle you have already collected provides a starting point for that work.
Read more: chain of custody for digital evidence.