
Screenshot as evidence: how to capture it, step by step
A screenshot taken with a phone or the Print Screen key is an image file: it opens in any graphics program, can be retouched in a minute, and does not, on its own, establish when it was taken, on which computer or by whom. If the person receiving it disputes it, it falls to whoever produced it to show that it is genuine, and the image file alone provides little supporting information.
To capture it as evidence, the software captures the image and performs the subsequent checks as part of a single automated process: it produces the image, immediately computes its hashes, applies a timestamp to it and seals it in a bundle anyone can verify. That is what the Screenshot module of C.E.R.T.O. does.
Before you start: is this the right tool?
It depends on where the content you want to capture is.
- It is on your screen right now (a window, a program, an error message, a video call): use the Screenshot module. That is the case this guide covers.
- It is a page that is still online (a site, a post, a review): the Web pages module is the better choice, because besides screenshots it keeps the page code, the address, the site certificate and HTTP traffic (HAR). The procedure is in the guide on capturing a web page.
- You already took the screenshot: the file can be recorded with the Images module. To be clear: from that moment the file is documented and cannot change unnoticed, but this acquisition does not establish when or where the original screenshot was taken.
What you need
- C.E.R.T.O. Desktop installed (Windows x64 or macOS Apple Silicon) and an account with a confirmed email address.
- 1 slot per screenshot; 3 slots if you add the InfoCert qualified timestamp.
- Whatever you want to capture, already open and clearly visible on screen.
The procedure in six steps
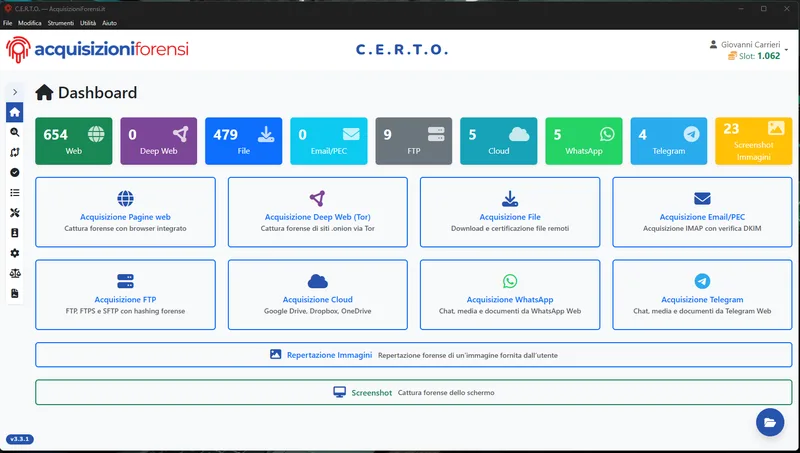
Step 1. Open C.E.R.T.O. and click "Screenshot"
On the dashboard, click "Screenshot", the bar labelled "Forensic screen capture". The capture page opens, listing the connected displays.
Step 2. Prepare the content you want to capture
Bring the window you need to the front. Close or minimise everything unrelated: whatever is on screen ends up in the evidence, including notifications, other chats and browser tabs.
Step 3. Select the monitor
Under "Select monitor" the software lists the connected displays, each with a preview and its native resolution. Pick the right one; if there is only one, it is already selected. A notice tells you that the C.E.R.T.O. window will be hidden during the capture. The full list of detected displays is written into the bundle in any case.
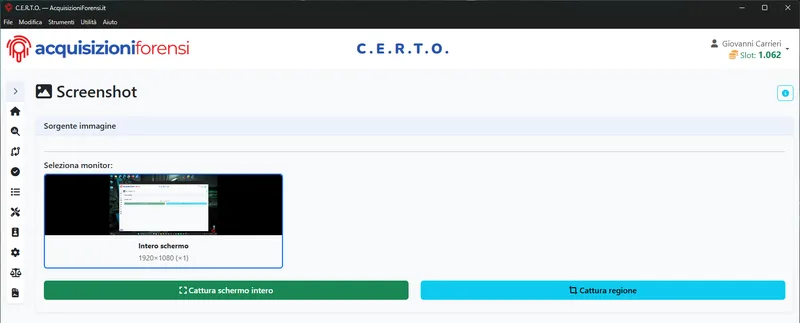
Step 4. Click "Capture full screen" or "Capture region"
Full screen also shows the context (system bar, clock, other windows). A region isolates one part. When in doubt, go full screen: context provides additional information for assessing the image.
The capture happens the moment you click the button. The C.E.R.T.O. window hides and the image is produced by the operating system's capture functions at the display's native resolution. The software immediately computes its SHA-256 hash, while the image is still in memory. In the same operation it measures the clock offset against several NTP servers and records the state of the computer: user, machine name, operating system, displays.
Step 5. Check the preview and decide whether to add the InfoCert timestamp
The software shows the "Image preview". If it is not what you wanted, click "Back" and capture again.
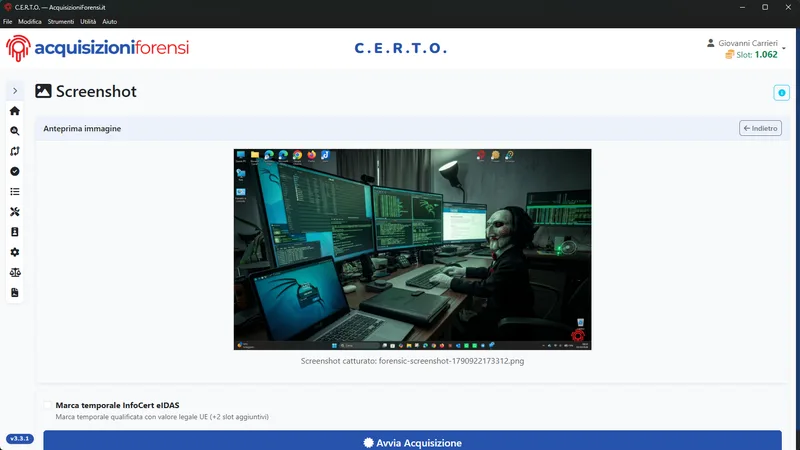
The timestamp checkbox is below the preview. By default the bundle receives two RFC 3161 timestamps from non-qualified timestamping authorities, at no extra cost. Ticking "InfoCert eIDAS timestamp" (+2 slots) adds a qualified one: under the eIDAS regulation it enjoys a presumption of accuracy of the date and time and of integrity of the timestamped data.
Step 6. Click "Start Acquisition" and let the software do the rest
From this point on, the procedure is automatic. The image does not open in an editor and does not go through a "Save As" step. First the software recomputes the SHA-256 hash of the file and compares it with the one computed at capture: if they do not match, it stops. Then it:
- computes the MD5, SHA-1, SHA-256 and SHA-512 hashes and the perceptual hashes;
- writes into the bundle the state of the computer recorded at capture;
- analyses the image and generates a watermarked copy next to the original;
- signs the manifest with the device's Ed25519 key, applies the timestamps and seals everything in a BagIt bundle.
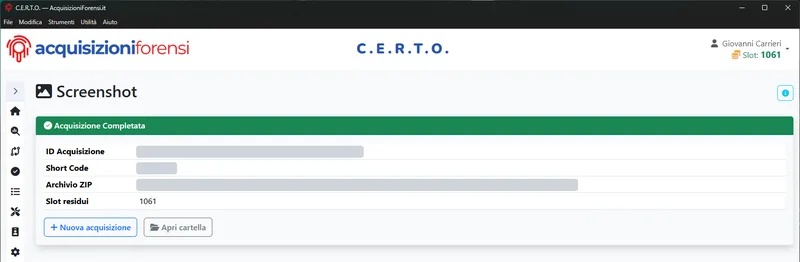
What you end up with
A ZIP file, the bundle, containing:
- the captured image as it is, and the watermarked copy, each with its own hashes;
- the list of displays and the state of the computer at capture time;
- the report as PDF and plain text;
interactive.html, a dashboard that opens with a double click even on a computer without C.E.R.T.O.;verify.shandverify.bat, which recompute the hashes and verify the signature and timestamps.
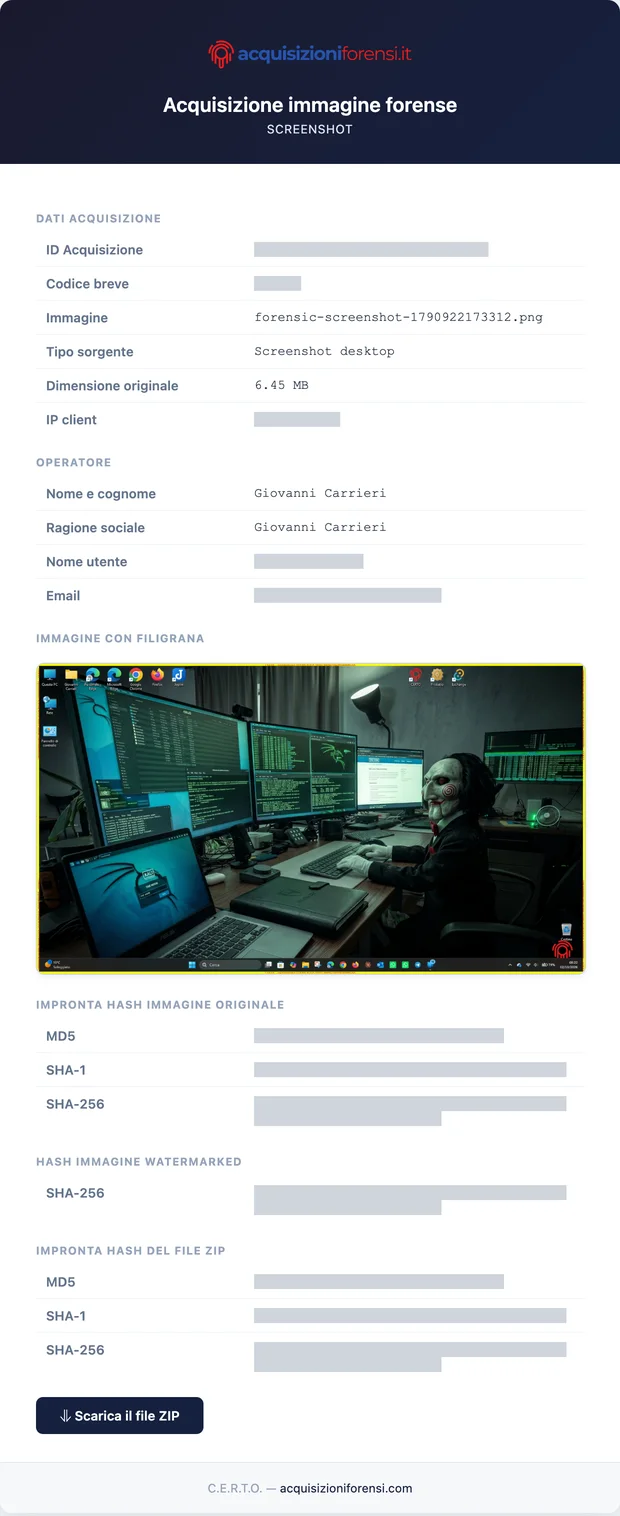
When the procedure ends you also receive a confirmation email. It shows:
- the acquisition identifier and short code;
- the operator's details;
- the watermarked copy of the image;
- the hashes of the image and of the ZIP file;
- the link to download the bundle.
The six-character short code is also on the report: whoever receives it can look it up in the public registry, from the Find an acquisition page, and open the report online.
By hand or with C.E.R.T.O.
| By hand | With C.E.R.T.O. | |
|---|---|---|
| Who produces the image | You, with a key | The system, no intervention |
| Can it be retouched first? | Yes, leaving no trace | The hash is computed at capture and rechecked before the bundle is sealed: if the file has changed, the procedure stops |
| When it was taken | The file date, which can be edited | Measured NTP time + timestamps |
| On which computer | Not recorded | User, machine, system and displays in the bundle |
| Later changes | The file alone does not allow this check | Changes to the checked files cause hash verification to fail |
| Can the recipient verify it? | The file alone provides little supporting information | They recompute the hashes themselves |
How the recipient verifies it
The hashes can be recomputed with tools already present in the operating system, without C.E.R.T.O. and without a network connection. To check the signature and the timestamps as well, run the included script (sh verify.sh on macOS and Linux, verify.bat on Windows), which requires OpenSSL 3. The process is described in the guide How the opposing party can verify digital evidence.
What it proves, and what it does not
The bundle shows that this image was on the screen of that computer at that time and has not changed since. It does not show that what the screen displayed was true: a page may have been altered beforehand, a chat may belong to another account. That is why, when the content is online, acquiring it at the source with the Web pages module is stronger. The court decides how much weight to give the evidence. The bundle provides information that can be independently checked.
Frequently asked questions
How much does it cost to capture a screenshot with C.E.R.T.O.?
1 slot per screenshot, 3 with the InfoCert qualified timestamp. A slot costs from €6 down to €3 depending on the slot package; you get 2 free when you confirm your email. Current prices are on the pricing page.
Can I use a screenshot I have already taken?
Yes, with the Images module, with one limit you should know: the file is documented from that moment on. This acquisition does not establish when or where the original screenshot was taken.
Is a screenshot of a WhatsApp chat good enough?
It captures what is visible on screen, not the conversation. For a chat the WhatsApp module is more complete: it acquires messages, media and metadata.
Do I need the InfoCert timestamp?
It is optional. The two default timestamps establish a time reference for the bundle; the InfoCert one is eIDAS-qualified and enjoys a presumption of accuracy of date and time. It is worth it when the date is the point you expect to be challenged.
Can I capture a second monitor, or only part of the screen?
Yes: pick any connected display, full screen or a region.
Glossary of terms
- Screenshot: an image of the entire screen or part of it, produced by the device's capture functions.
- Acquisition: a procedure for collecting content and documenting information that supports later verification.
- Cryptographic hash: a value computed from a file's contents. Recomputing it and comparing it with the recorded value allows you to check whether the file has remained identical.
- MD5, SHA-1, SHA-256 and SHA-512: algorithms that compute hashes. MD5 and SHA-1 are older algorithms with known security limitations; they should not be used alone as a cryptographic guarantee of integrity.
- Perceptual hash: a value that describes an image's visual features and helps compare similar images. It does not replace a cryptographic hash when checking file integrity.
- Integrity: a match between a file's contents and those recorded at acquisition time. It does not imply that what the file shows is true.
- NTP (Network Time Protocol): a protocol used to compare a computer's clock with reference servers. The offset is the difference between the local time and the servers' time.
- Timestamp: an attestation that links a hash to a date and time. It helps document that the data represented by the hash existed by that time.
- RFC 3161: the technical specification for the protocol used to request and receive timestamps.
- Timestamping authority (TSA): a service that issues signed timestamps.
- Qualified electronic timestamp: a timestamp issued by a qualified provider under the eIDAS regulation. In this article, it is the option provided by InfoCert.
- eIDAS: the European Union regulation governing electronic identification and trust services, including electronic timestamps.
- Manifest: a file listing the bundle's files and their hashes, used to check their integrity.
- Ed25519 signature: a cryptographic signature produced with a private key and verifiable with the corresponding public key. Here, it is applied to the manifest using the device's key; it does not, by itself, identify the person who performed the acquisition.
- BagIt bundle: a collection of files, metadata and manifests organised according to the BagIt format. The hashes in the manifests allow the integrity of the listed files to be checked.
- Metadata: information describing content or the circumstances of its acquisition, such as the operating system and the display used.
- Native resolution: the number of pixels used by a display at its intended resolution.
- Watermark: visible text or a mark added to a copy of the image. In the bundle, the watermarked copy is separate from the original.
- HTTP traffic (HAR): a log of the browser's HTTP requests and responses, saved in the HTTP Archive format. It is not a capture of all network traffic.
- OpenSSL 3: software providing cryptographic tools, used by the scripts mentioned here to verify the signature and timestamps.
- Slot: a unit of C.E.R.T.O. credit consumed by an acquisition or an additional option. The number required depends on the module and the selected options.
Register for free: the 2 welcome slots are enough for your first two screenshots.
Read more: what the chain of custody of digital evidence is.